Security
Build trust around your email operations, not just your email design.
Security in beensend is about protecting account access, managing sender related trust, and supporting workflows that are safer for teams and subscribers. It helps teams operate more confidently as they grow.
See pricingContact us
Service scope: beensend is for permission-based marketing campaigns only. Bulk/mass email blasts, transactional/system messages and campaigns to purchased or non-consenting lists are not allowed. Read acceptable use · Terms & conditions
Infrastructure transparency
Built on AWS infrastructure.
Designed for your email workflows.
beensend uses Amazon Web Services (AWS) infrastructure to host its platform. We believe customers should know which cloud provider supports their email marketing workspace and what that means in practice.
Application hosting: beensend uses AWS as the cloud hosting foundation for its SaaS platform.
Your daily workflow: Create campaigns, manage contacts and monitor performance from the beensend dashboard.
Delivery transparency: Email delivery depends on the configured sending service and verified sender setup, not on AWS hosting alone.
Explore our infrastructure ↗Security and privacy details
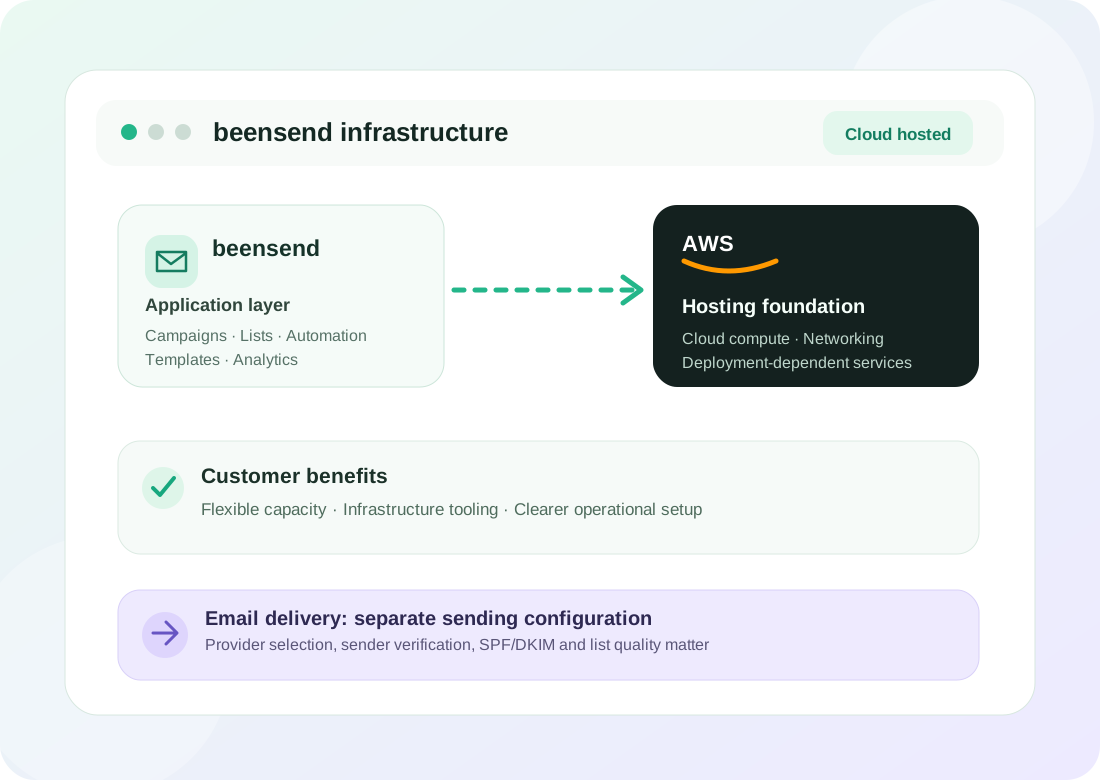
AWS is the infrastructure provider. Specific hosting region, processing locations, contractual commitments and certifications should be confirmed through beensend support.
Quick answer
What do SPF, DKIM and DMARC do?
SPF lists authorized sending sources, DKIM authenticates signed messages, and DMARC adds alignment and reporting policy. Google requires SPF or DKIM for all senders and SPF, DKIM and DMARC for bulk senders to personal Gmail accounts.
Browse email marketing FAQs ↗Overview
Cloud security, account security and sender trust
beensend uses AWS as its application hosting foundation. The product layer, email delivery route, compliance duties and customer responsibilities are separate. Explore the specific details below.
Shared responsibility in the AWS cloud
AWS is responsible for protecting the physical and underlying infrastructure of AWS cloud services. beensend is responsible for how its application is configured and administered, including suitable access management, secure deployment, application maintenance and customer-data handling.
Sender authentication and abuse prevention
Sending-domain verification, SPF, DKIM and DMARC help mailbox providers validate sender identity and identify unauthorized use. Accurate DNS settings and healthy sender reputation influence delivery more directly than the cloud-hosting brand.
Operational resilience and incident handling
AWS offers cloud building blocks for monitoring, backups and resilient deployment, but these measures only apply when configured and maintained. beensend should assess access logs, application updates, service health, backup restoration and incident-response procedures within its own deployment.
Security
Shared responsibility in the AWS cloud
AWS is responsible for protecting the physical and underlying infrastructure of AWS cloud services. beensend is responsible for how its application is configured and administered, including suitable access management, secure deployment, application maintenance and customer-data handling.
Customers remain responsible for credentials they control, their audience permissions, campaign content and domain DNS configuration. AWS compliance programs cannot be described as independent beensend certification.
- AWS protects infrastructure of the cloud
- beensend manages security in its deployment
- Customers secure access and authorized sending
Security
Sender authentication and abuse prevention
Sending-domain verification, SPF, DKIM and DMARC help mailbox providers validate sender identity and identify unauthorized use. Accurate DNS settings and healthy sender reputation influence delivery more directly than the cloud-hosting brand.
Mailing unconsented lists, ignoring bounces or changing sending domains without validating DNS can harm deliverability even with reliable cloud infrastructure.
- Authenticate domains with SPF and DKIM
- Publish an appropriate DMARC policy
- Monitor complaints, bounces and unsubscribe activity
Security
Operational resilience and incident handling
AWS offers cloud building blocks for monitoring, backups and resilient deployment, but these measures only apply when configured and maintained. beensend should assess access logs, application updates, service health, backup restoration and incident-response procedures within its own deployment.
Specific uptime, recovery-time objectives, certifications and storage-region commitments should be published only after operational validation.
- Review backups and recovery testing
- Control privileged access and updates
- Document incident contact and escalation
Highlights
Practical benefits and responsibilities
Transparent cloud hosting, correctly configured email delivery and responsible data handling help teams make better decisions.
See the setup
Understand key sending controls instead of hiding them behind guesswork.
Build trust
Support a more reliable foundation for ongoing campaign delivery.
Reduce oversights
Make routine operational checks easier to complete.
Frequently asked questions
Questions people may ask on this topic.
Short answers help visitors move faster without losing clarity.
What does security include in beensend?
Security in beensend is explained here through practical use cases, clearer structure, and page specific visuals so teams can understand what the capability actually helps them do.
How is this different from a basic email workflow?
The focus is on practical workflow value, not just feature labels. The copy explains how the capability supports clearer operations, better collaboration, and stronger email execution.
Can this page help before I contact sales or support?
Yes. The page is written to answer common pre sales and product understanding questions, and you can contact the team if you need a more tailored explanation.
Need a clearer walkthrough?
If you want help understanding where this part of beensend fits into your workflow, contact the team and we can guide you.
DATA SECURITY & PRIVACY
Security built around responsible email operations.
Protecting customer data involves the right account practices, sender verification, infrastructure controls and transparent privacy expectations. beensend provides the visible sending and account workflows below; specialized certifications are not claimed unless independently confirmed.
Account access and roles
Manage platform roles and account permissions to support a safer work environment for teams. Assign access according to operational responsibilities.
Sender authentication
Configure verified senders and sending domains. Use SPF and DKIM DNS records with your email delivery provider to support authenticated sending.
Permission-based marketing
Maintain consent-driven subscriber practices, unsubscribe handling and suppression controls that support a responsible sending environment.
Operational visibility
Review sending health, campaign metrics and domain configuration as part of regular account maintenance and deliverability preparation.
COMPLIANCE GUIDE
GDPR, HIPAA and CSA: what they mean for your email setup
GDPR focuses on lawful handling of personal data and individual rights. HIPAA applies to certain US healthcare entities and business associates. CSA is an industry sender certification program. These standards have different eligibility requirements, and none should be treated as automatic compliance from simply using email software.
For beensend, any specific certification, HIPAA-ready use or GDPR compliance claim must be supported by reviewed processes, infrastructure commitments, agreements and evidence before being advertised.
Read our privacy overview →Key trust topics
Understand the difference between a feature, a provider capability and a verified certification.
Identity checksVerified senders
Domain setupSPF / DKIM
SubscribersConsent and suppression
Account managementRoles and visibility